Windows Updates / Patch Tuesday
Keeping Windows Updated: Why Patch Tuesday Actually Matters “I’ll update it later” is one of the most common — and

Keeping Windows Updated: Why Patch Tuesday Actually Matters “I’ll update it later” is one of the most common — and
Strong Passwords and Windows Hello: A Practical Setup Guide Passwords remain the weakest link in most people’s security setup —
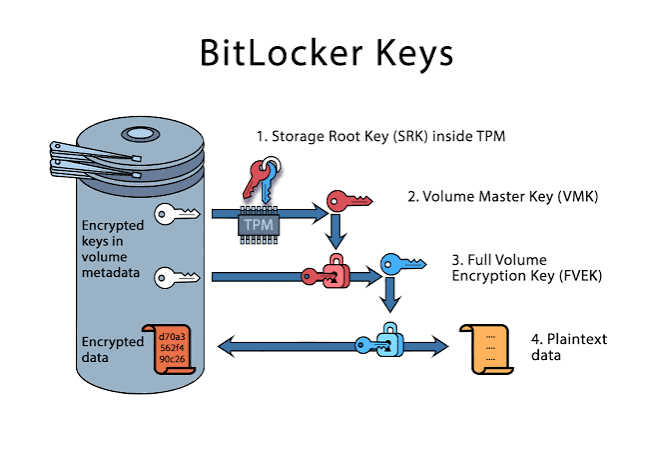
Setting Up BitLocker to Encrypt Your Windows Drive If your laptop were lost or stolen tomorrow, would whoever found it
How to Spot a Phishing Email Before It Costs You Phishing remains one of the most effective attack methods in
Why You Should Enable Windows Defender Firewall (and How to Do It Right) If you’ve ever skipped past a firewall
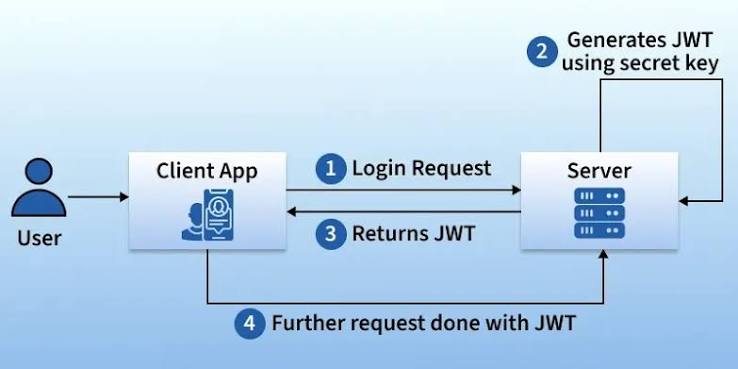
JWT Security: Common Vulnerabilities and How to Exploit (and Fix) Them JSON Web Tokens (JWTs) are a widely used way
SSRF (Server-Side Request Forgery) Explained: How Attackers Abuse Trust Server-Side Request Forgery (SSRF) happens when an attacker can make a
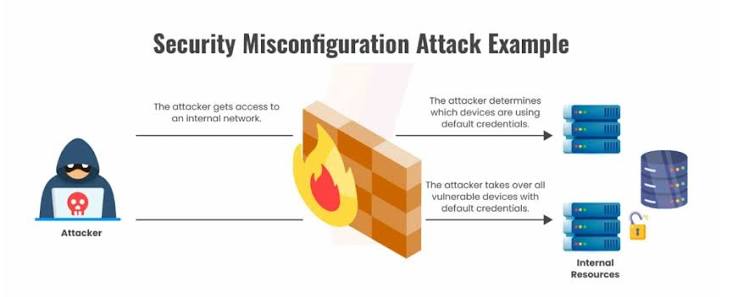
Security Misconfiguration: The Silent Web Vulnerability Nobody Talks About Security Misconfiguration isn’t one specific bug — it’s a whole category
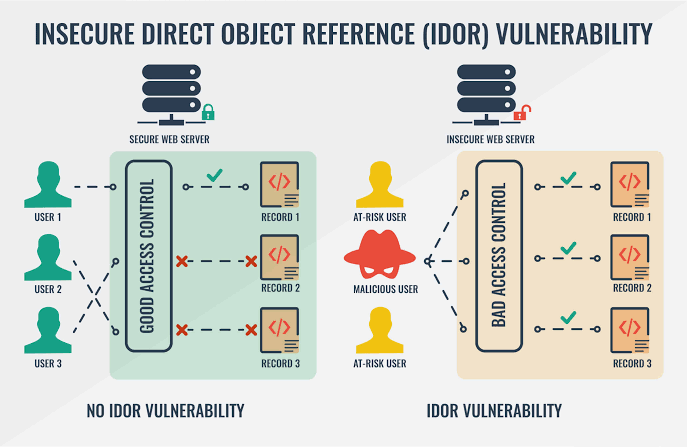
Insecure Direct Object References (IDOR): A Beginner’s Guide An Insecure Direct Object Reference (IDOR) happens when an application exposes a
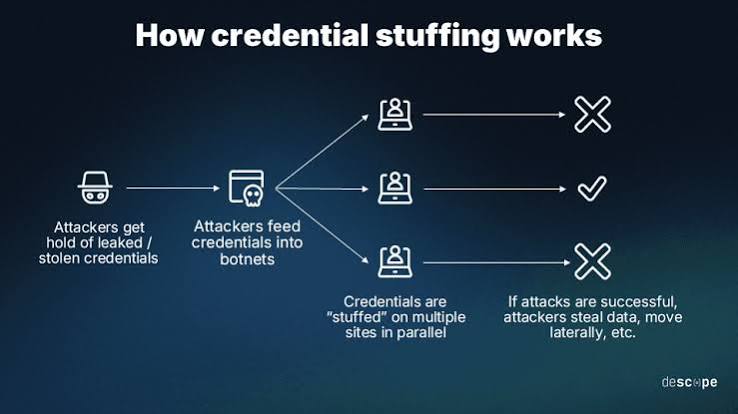
Broken Authentication: The #1 Web Vulnerability and How Attackers Exploit It Broken Authentication covers a whole category of flaws in