How to Build a Blue Team Home Lab: Wazuh, Sysmon and Atomic Red Team
Why a home lab matters, a minimal useful setup, and how to practice detection realistically. Module 20 of The Complete Blue Team Course.
Deep dives and cheat sheets for the tools security professionals rely on — Nmap, BloodHound and more — with the commands and workflows that actually matter in real engagements.
Why a home lab matters, a minimal useful setup, and how to practice detection realistically. Module 20 of The Complete Blue Team Course.
Active Directory is the backbone of almost every enterprise network. It handles authentication, authorization, group policies, and trust relationships across
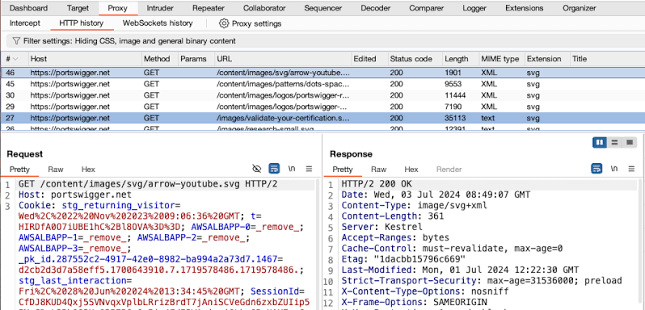
1. Introduction Burp Suite is one of the most widely used tools in web application penetration testing. Security professionals use
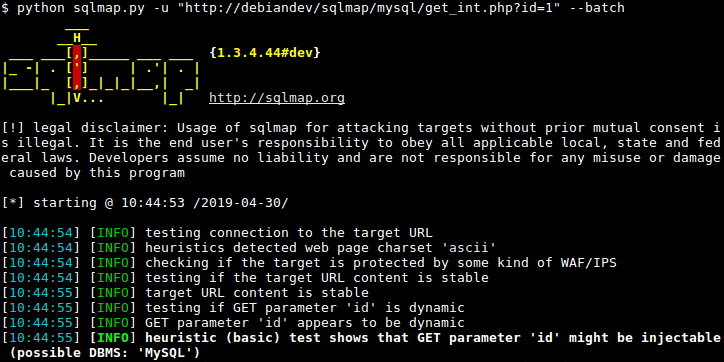
SQLmap is an open-source command-line tool that automates the detection and exploitation of SQL injection flaws. In a penetration test,
This Nmap cheat sheet gives you the commands you actually use during a pentest, a CTF or a network audit: