>_ the cyber track
Cyber Track Blog
Write-ups, attack paths and defensive notes on Active Directory, Linux, Windows and web security.
Featured articles
-
Linux Log Analysis for Defenders: auth.log, journalctl, and auditd
The Linux security model, where Linux logs live, and how auditd turns a server into a system you can investigate. Module 5 of The Complete Blue Team Course.
-
What Is a SIEM? Log Management and Security Monitoring Explained
What a SIEM actually does, how to write queries that matter, and how to manage log…
-
MITRE ATT&CK for Defenders: Mapping Detections to Techniques
How blue teams use MITRE ATT&CK to describe attacker behavior, track detection coverage, and build detections…
-
Threat Intelligence for Defenders: Turning Intel into Detections
What threat intelligence is for, the strategic, operational and tactical levels, and how defenders turn intel…
Browse all articles
-
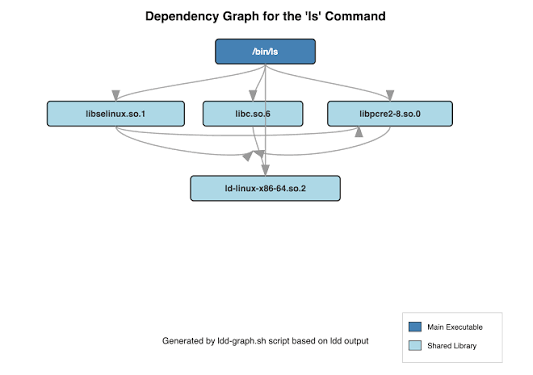
Linux Shared Library Security: LD_PRELOAD, RPATH, RUNPATH, and Dynamic Linking Risks
1. Introduction Linux Shared Library Security: LD_PRELOAD, RPATH, RUNPATH, and Dynamic Linking Risks is an advanced Linux security topic because the dynamic…
-
Linux Privilege Escalation Through PATH, Environment Variables, and Unsafe Executables
1. Introduction Linux Privilege Escalation Through PATH, Environment Variables, and Unsafe Executables is an advanced Linux security topic because privileged scripts can…
-
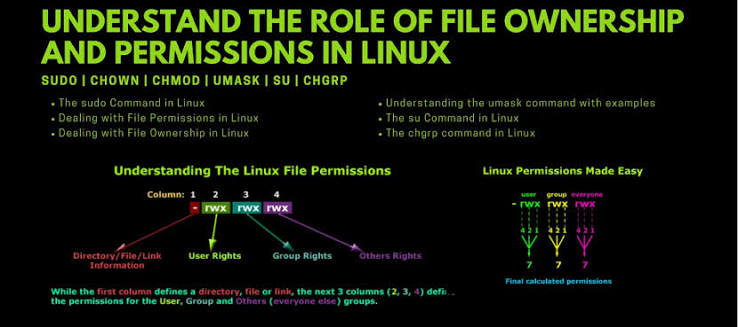
Advanced Linux File Security: ACLs, Extended Attributes, Immutable Files, and xattrs
1. Introduction Advanced Linux File Security: ACLs, Extended Attributes, Immutable Files, and xattrs is an advanced Linux security topic because ACLs and…
-
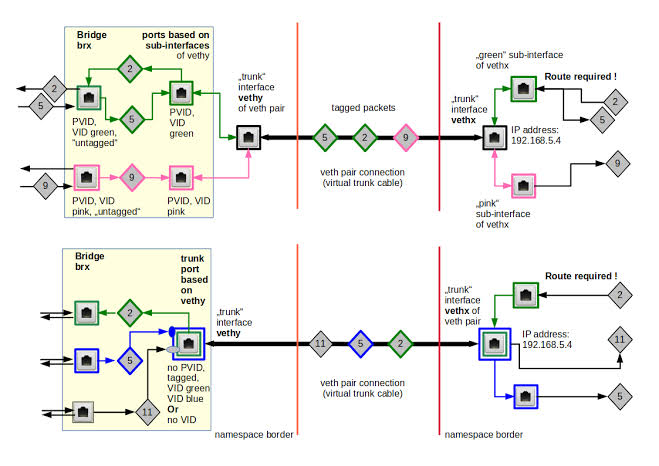
Linux Network Namespaces and Virtual Networking: veth, Bridges, Routing, and Security
1. Introduction Linux Network Namespaces and Virtual Networking: veth, Bridges, Routing, and Security is an advanced Linux security topic because network namespaces,…
-
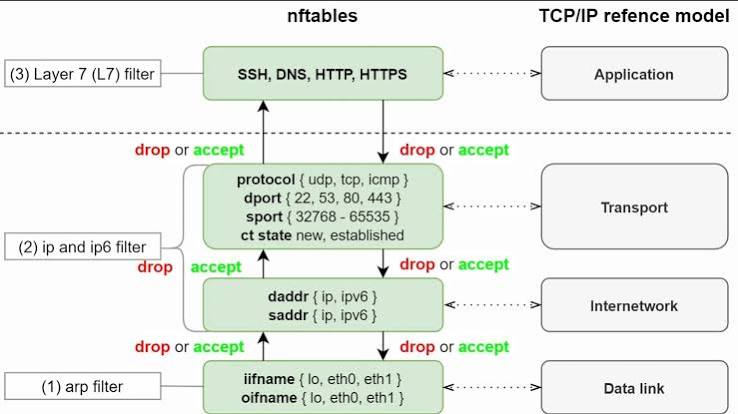
Advanced nftables: Stateful Filtering, Sets, Maps, NAT, and Network Segmentation
1. Introduction Advanced nftables: Stateful Filtering, Sets, Maps, NAT, and Network Segmentation is an advanced Linux security topic because nftables can implement…
-
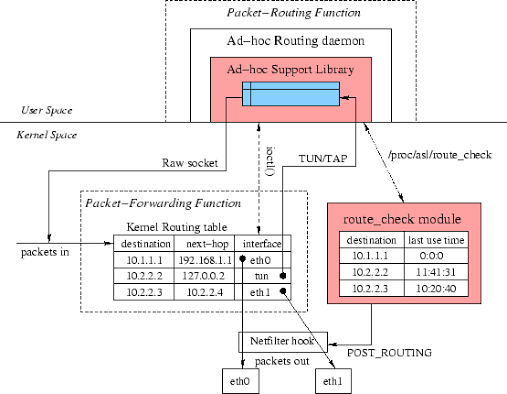
Linux Routing Security: Policy Routing, Reverse Path Filtering, ARP, and Neighbor Tables
1. Introduction Linux Routing Security: Policy Routing, Reverse Path Filtering, ARP, and Neighbor Tables is an advanced Linux security topic because Linux…
-
Linux Memory Security: ASLR, NX, PIE, Stack Canaries, and Kernel Protections
1. Introduction Linux Memory Security: ASLR, NX, PIE, Stack Canaries, and Kernel Protections is an advanced Linux security topic because ASLR, NX,…
-
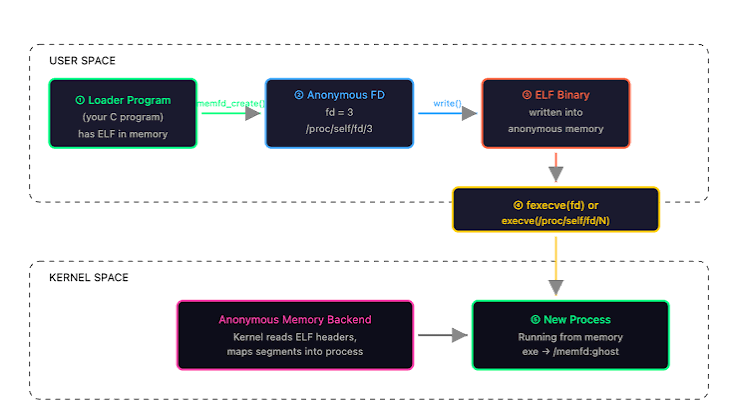
Advanced Linux Forensics: Deleted Files, /proc, File Descriptors, and Memory Artifacts
1. Introduction Advanced Linux Forensics: Deleted Files, /proc, File Descriptors, and Memory Artifacts is an advanced Linux security topic because volatile Linux…
-
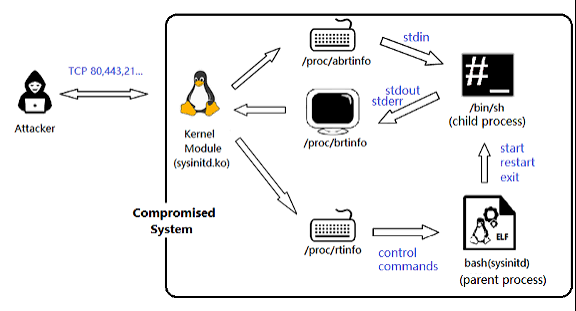
Linux Rootkit Detection: Processes, Kernel Modules, Hooks, and Integrity Verification
1. Introduction Linux Rootkit Detection: Processes, Kernel Modules, Hooks, and Integrity Verification is an advanced Linux security topic because rootkits attempt to…