>_ the cyber track
Cyber Track Blog
Write-ups, attack paths and defensive notes on Active Directory, Linux, Windows and web security.
Featured articles
-
Linux Log Analysis for Defenders: auth.log, journalctl, and auditd
The Linux security model, where Linux logs live, and how auditd turns a server into a system you can investigate. Module 5 of The Complete Blue Team Course.
-
What Is a SIEM? Log Management and Security Monitoring Explained
What a SIEM actually does, how to write queries that matter, and how to manage log…
-
MITRE ATT&CK for Defenders: Mapping Detections to Techniques
How blue teams use MITRE ATT&CK to describe attacker behavior, track detection coverage, and build detections…
-
Threat Intelligence for Defenders: Turning Intel into Detections
What threat intelligence is for, the strategic, operational and tactical levels, and how defenders turn intel…
Browse all articles
-
PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Critical PHP RCE Explained, Detection and Mitigation
PHP2Shell (CVE-2026-109618 & CVE-2026-109619) is a critical unauthenticated RCE in the PHP core. Learn which versions are affected, how to patch, verify…
-
Windows Active Directory Attacks: A Practical Guide for Penetration Testers
Active Directory is the backbone of almost every enterprise network. It handles authentication, authorization, group policies, and trust relationships across thousands of…
-
HTB Stream Writeup — Hack The Box Season 12
HTB Stream — Full Writeup An Insane-rated Linux box built around a real-world airline data pipeline. The attack chains XXE injection, Kafka credential exfiltration,…
-
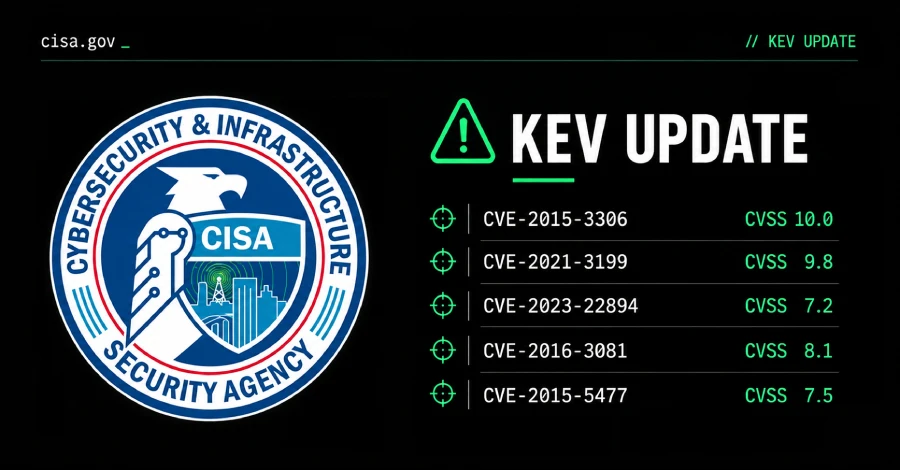
Flax Typhoon Exploits Five Old Flaws: CISA KEV Update and What to Patch
In short: CISA has added five actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after a joint advisory linked them…
-
CVE-2026-104286: FortiMail Zero-Day Exploited for Unauthenticated File Writes
In short: CVE-2026-104286 is a critical (CVSS 9.8) path traversal vulnerability in Fortinet FortiMail that lets an unauthenticated attacker write arbitrary files…
-
NeedyMantis Malware: China-Linked Backdoor Built for Long-Term Network Access
In short: Microsoft Threat Intelligence has documented NeedyMantis, a previously unknown modular backdoor used after attackers already have a foothold, to keep…
-
CVE-2026-61500: Rejetto HFS Session Forgery Leads to RCE as Scanning Begins
In short: CVE-2026-61500 is a critical (CVSS 9.3) authentication bypass in Rejetto HTTP File Server (HFS) 3.x. Because the server’s session-signing key…
-
Pixel 10 Hacked Three Times at Pwn2Own Ireland 2026: What We Know
In short: Google’s Pixel 10 was successfully attacked three times on October 8, 2026, during Pwn2Own Ireland in Cork, even though contest…
-
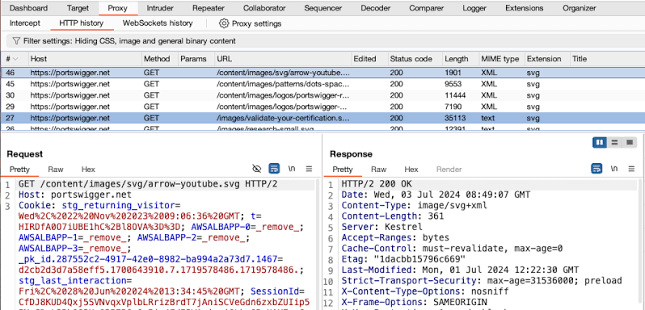
Burp Suite for Web Penetration Testing: Proxying, Repeater, Intruder
1. Introduction Burp Suite is one of the most widely used tools in web application penetration testing. Security professionals use it to…