>_ the cyber track
Cyber Track Blog
Write-ups, attack paths and defensive notes on Active Directory, Linux, Windows and web security.
Featured articles
-
Linux Log Analysis for Defenders: auth.log, journalctl, and auditd
The Linux security model, where Linux logs live, and how auditd turns a server into a system you can investigate. Module 5 of The Complete Blue Team Course.
-
What Is a SIEM? Log Management and Security Monitoring Explained
What a SIEM actually does, how to write queries that matter, and how to manage log…
-
MITRE ATT&CK for Defenders: Mapping Detections to Techniques
How blue teams use MITRE ATT&CK to describe attacker behavior, track detection coverage, and build detections…
-
Threat Intelligence for Defenders: Turning Intel into Detections
What threat intelligence is for, the strategic, operational and tactical levels, and how defenders turn intel…
Browse all articles
-
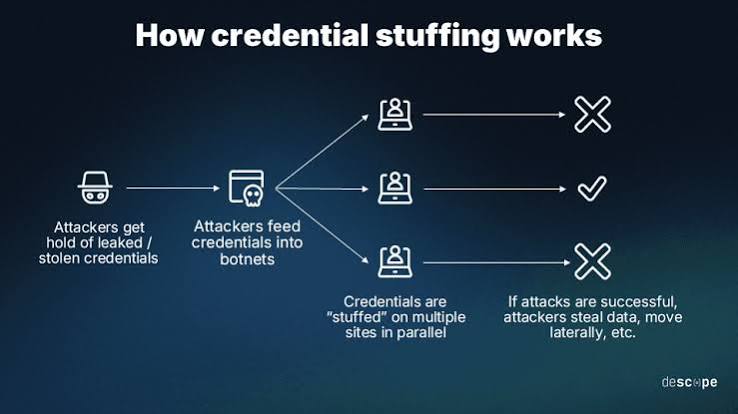
Broken Authentication
Broken Authentication: The #1 Web Vulnerability and How Attackers Exploit It Broken Authentication covers a whole category of flaws in how an…
-
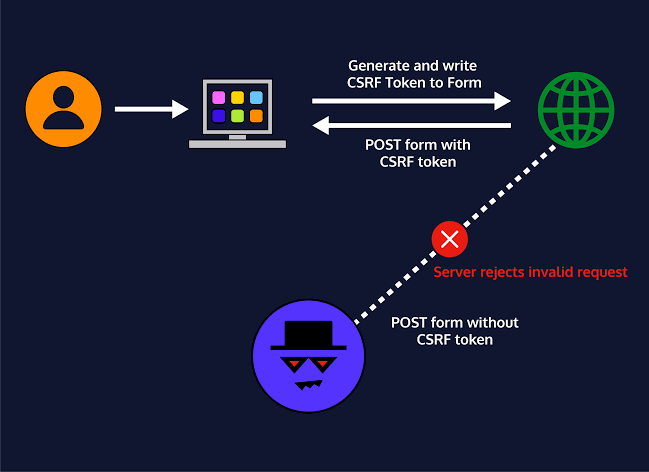
What Is CSRF?
What Is CSRF? Cross-Site Request Forgery Explained with Examples Cross-Site Request Forgery (CSRF) tricks a logged-in user’s browser into sending a request…
-
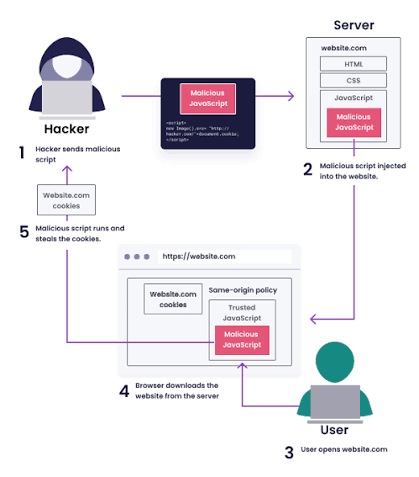
Cross-Site Scripting (XSS)
Cross-Site Scripting (XSS): Types, Examples, and How to Fix It Cross-Site Scripting (XSS) happens when an application allows an attacker to inject…
-
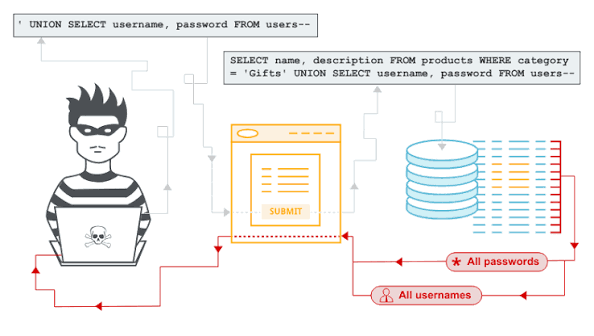
SQL Injection
SQL Injection Explained for Beginners: How It Works and How to Prevent It SQL Injection (SQLi) is one of the oldest and…
-
HTB Layover Writeup — Hack The Box Season 12
HTB Layover — From Open WiFi to Root: A Full Attack-Chain Breakdown Machine: Layover · Platform: Hack The Box · Season: 12 · OS: Linux (Ubuntu 24.04 container) This…
-
Shellshock (CVE-2014-6271): Detection and Mitigation Guide
CVE-2014-6271 Shellshock is a remote command execution vulnerability affecting GNU Bash. It became one of the best-known security flaws of its time…
-
CVE-2014-6271 Shellshock
CVE-2014-0160 Heartbleed is a information disclosure vulnerability affecting OpenSSL. It became one of the best-known security flaws of its time because the…
-
Active Directory Domain Trusts: Direction, Transitivity, SID Filtering, and Blast Radius
How AD trusts define security boundaries: parent/child, forest and external trusts, direction, transitivity, SID filtering and selective authentication, plus commands to enumerate,…
-
DNS and Active Directory: SRV Records, Dynamic Updates, and Spoofing Risks
How AD-integrated DNS, SRV records and dynamic updates underpin authentication, why insecure updates and record takeover matter, and how to audit AD…